Openvpn tls handshake failed heres how to fix it like a pro
Openvpn tls handshake failed heres how to fix it like a pro. Quick fact: TLS handshake failures are usually caused by certificate mismatches, outdated crypto, or server-client configuration issues. This guide walks you through a clear, step-by-step approach to diagnose and fix the problem, plus tips to prevent it from happening again.
- Quick fixes you can try right now:
- Check your time and date on both client and server.
- Verify certificates and keys haven’t expired.
- Confirm you’re using compatible TLS versions and cipher suites.
- Reboot the VPN service on both ends.
- Review logs for specific error messages and search them for targeted fixes.
In this article, you’ll learn:
- What TLS handshakes are in OpenVPN and why failures occur
- Common misconfigurations that trigger handshake errors
- Step-by-step diagnostic checklist with practical commands
- How to fix certificate, keys, and CA issues
- Server and client configuration examples
- Advanced troubleshooting for stubborn cases
- Security best practices to prevent future TLS problems
- Resources and tools to keep handy
Introduction: what you’ll get and quick facts
- What happens during a TLS handshake: The client and server exchange certificates, verify identities, and negotiate encryption parameters before data starts flowing. If anything in this chain doesn’t line up, you’ll see a handshake failure.
- Common root causes include mismatched TLS versions, certificate validation failures, outdated OpenVPN binaries, and firewall or NAT interference.
- The fix usually involves a combination of certificate checks, configuration alignment, and ensuring both sides are speaking the same protocol language.
Useful URLs and Resources text only Apple Website - apple.com Artificial Intelligence Wikipedia - en.wikipedia.org/wiki/Artificial_intelligence OpenVPN Community - openvpn.net TLS/SSL Training - www.cloudflare.com/learning/ssl/what-is-tls/ RFC 5246 - tools.ietf.org/html/rfc5246 OpenSSL Documentation - openssl.org/docs/ VPN Security Best Practices - resources.cdn.mozilla.net/
Table of contents
- Quick diagnosis checklist
- Understanding TLS handshakes in OpenVPN
- Common causes of TLS handshake failures
- Step-by-step fix guide
- Certificate and key management
- Server-side configuration tips
- Client-side configuration tips
- Network and firewall considerations
- Logging and troubleshooting techniques
- Security best practices
- FAQ
Quick diagnosis checklist
- Check system clocks: both ends should be within a few minutes of each other.
- Verify CA, cert, and key files: ensure the client cert matches the server’s CA and that the key pair is correct.
- Confirm the server config: TLSVersion, cipher settings, and cert paths are consistent with the client.
- Review logs: OpenVPN logs often point to the exact misconfiguration, like “CERTIFICATE_VERIFY_FAILED” or “tlsHandshake”.
Understanding TLS handshakes in OpenVPN
- The client and server perform a multi-step exchange: authenticate the server, verify the client certificate, exchange session keys, and establish a secure tunnel.
- If any step fails, you’ll see a specific error, such as:
- TLS Error: tlsv1 alert unknown ca
- TLS Error: TLS key negotiation failed to occur within a specific time or no ciphers available
- AUTH: Received control message: AUTH_FAILED
- Knowing the typical error messages helps you target the fix fast.
Common causes of TLS handshake failures
- Time drift between client and server clocks
- Expired or misconfigured certificates CA, server cert, or client cert
- Mismatched TLS versions or cipher suites
- Incorrect file permissions or corrupted certificate files
- Firewall or NAT breaking the TLS handshake traffic
- Incorrect port or server address
- OpenVPN daemon not running or misconfigured server
- Client config pointing to a wrong CA or server cert
Step-by-step fix guide
- Verify time synchronization
- On Linux: sudo timedatectl status
- On Windows: Date and Time settings, ensure “Set time automatically” is on
- Check certificates
- Confirm CA certificate matches the server’s CA
- Confirm server certificate is valid and not expired
- Confirm client certificate is issued by the same CA
- Compare TLS settings
- Ensure both sides use the same TLS version TLSv1.2 or TLSv1.3 if supported
- Align cipher suites
- Inspect OpenVPN server and client configs
- Server: port, proto udp/tcp, dev tun/mtun, ca, cert, key, dh if using static DH
- Client: remote, dev, ca, cert, key, tls-auth or tls-crypt if used
- Test with verbose logging
- Client: openvpn --config client.ovpn --verb 4
- Server: grep -i "TLS" /var/log/openvpn.log
- Check network path
- Ensure UDP port default 1194 or the configured port is open
- Verify NAT traversal if behind a router
- Recreate certificates as a last resort
- Reissue CA, server, and client certificates
- Rebuild DH parameters if needed
- Try a clean reconnect test
- Restart OpenVPN service on both sides
- Reconnect to confirm the handshake completes
Certificate and key management
- Best practice: use short-lived certificates and rotate them regularly
- Store CA, server cert, and keys securely; limit access with proper permissions
- Use tls-auth or tls-crypt for an extra layer of security
- Check certificate revocation status if you suspect a compromised key
Server-side configuration tips
- Example server config simplified:
- port 1194
- proto udp
- dev tun
- ca ca.crt
- cert server.crt
- key server.key
- dh dh.pem
- server 10.8.0.0 255.255.255.0
- keepalive 10 120
- tls-auth ta.key 0
- cipher AES-256-CBC
- auth SHA256
- tls-version-min 1.2
- Ensure consistency with client config: same ca, certs, and keys, same TLS settings
Client-side configuration tips
- Example client config simplified:
- client
- dev tun
- proto udp
- remote your.vpn.server 1194
- resolv-retry infinite
- nobind
- persist-key
- persist-tun
- ca ca.crt
- cert client.crt
- key client.key
- tls-auth ta.key 1
- cipher AES-256-CBC
- auth SHA256
- verb 4
- If using TLS cryptography, ensure the ta.key is identical on both sides with correct direction
Network and firewall considerations
- Open the VPN port on firewall e.g., ufw allow 1194/udp or iptables rules
- Check for ISP or corporate firewalls blocking VPN traffic
- If behind a NAT, enable NAT traversal or use a VPN passthrough
- Consider switching from UDP to TCP to debug network issues though UDP is typical for performance
Logging and troubleshooting techniques
- Increase verbosity: set verb to 4 or 5 during troubleshooting
- Use status or log files to capture handshake events
- Look for common messages:
- TLS Error: tlsv1 alert unknown ca
- TLS Error: TLS key negotiation failed to occur within a certain time
- TLS Error: Cannot ioctl TUNSETIFF: Operation not permitted
- If you see certificate verification failures, recheck CA certificates and chain
- When in doubt, reissue certificates and rebuild configurations cleanly
Security best practices
- Use TLS 1.2 or higher; disable older insecure protocols
- Enable tls-auth or tls-crypt for mutual authentication
- Regularly rotate certificates and keys
- Enforce strong cipher suites and HMAC algorithms
- Keep OpenVPN and OS up to date with security patches
- Implement multi-factor authentication where possible
- Limit access with firewall rules and only allow necessary IP ranges
| VPN | From / month | Plan | Free plan | Refund | Alipay | UnionPay | Crypto | Website opens in China | Trustpilot | |
|---|---|---|---|---|---|---|---|---|---|---|
 NordVPN | $3.49/mo | 27 months: $94.23 | No | 30 days | ? | ✗ | ✓ | ✓ | ✗ Blocked | 4.2/5 (51,628 reviews) |
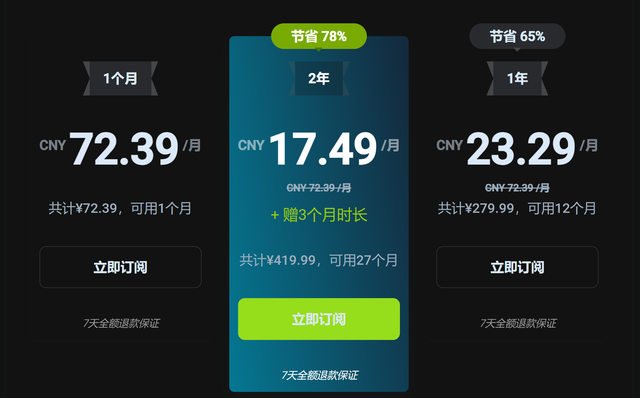
 ZoogVPN | $2.49/mo | 27 months: $59.99 | Yes | 7 days | ✓ | ✓ | ✓ | ✓ | ✓ Yes (2.5 s) | 4.2/5 (195 reviews) |
 ExpressVPN | $3.00/mo | 28 months: $84 | No | 30 days | ✗ | ✗ | ✓ | ✗ | ✗ Blocked | 4.4/5 (29,706 reviews) |
 Surfshark | See site | See site | No | 30 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.3/5 (31,823 reviews) |
 Proton VPN | $2.99/mo | 12 months: $35.88 | Yes | 30 days | ✗ | ✗ | ✗ | ✓ | ✓ Yes (2.5 s) | 2.1/5 (1,040 reviews) |
 Astrill VPN | $12.50/mo | 24 months: $300 | No | See site | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 1.3/5 (110 reviews) |
 Private Internet Access | $2.03/mo | 40 months: $81.2 | No | 30 days | ✗ | ✗ | ✗ | ✗ | ✗ Blocked | 4.2/5 (11,033 reviews) |
 CyberGhost | $2.19/mo | 28 months: $61.32 | No | 45 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.0/5 (24,178 reviews) |
 PureVPN | $1.69/mo | 60 months: $101.55 | No | 31 days | ? | ✗ | ✗ | ✓ | ✓ Yes (2.6 s) | 4.4/5 (17,994 reviews) |
 AdGuard VPN | $2.99/mo | 24 months: $71.76 | Yes | 30 days | ✓ | ✗ | ✓ | ✓ | Official site blocked; our special link opens (2.3 s) | 4.3/5 (290 reviews) |
 Mullvad | $5.61/mo | €5/mo | No | 14 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 3.2/5 (192 reviews) |
 Windscribe | $5.75/mo | 12 months: $69 | Yes | See site | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.7/5 (13,355 reviews) |
 StrongVPN | See site | See site | No | 30 days | ✓ | ✗ | ✗ | ✗ | ✗ Blocked | 4.4/5 (2,695 reviews) |
 LightXtreme 闪连 | $7.08/mo | 12 months: $84.99 | Yes | 30 days | ✓ | ✓ | ✓ | ✓ | ✓ Yes (2.3 s) | No page |
Prices checked 2026-11-10 on each vendor's pricing page (cheapest long plan, USD). Check the vendor's checkout for the final price.
Payment methods checked 2026-11-10 on each vendor's payment pages: all 14 take cards and PayPal; ✗ = not listed, ? = the vendor's own pages disagree.
China access: whether the official website opens from mainland China networks (tests the website only, not the VPN connection). Last checked 2026-11-11 04:07 Beijing time.
Trustpilot score and review count checked 2026-11-10.
FAQ
What is a TLS handshake error in OpenVPN?
A TLS handshake error occurs when the client and server cannot successfully establish a secure channel due to certificate, protocol, or network issues during the initial cryptographic handshake.
How do I check OpenVPN logs for handshake failures?
Look in the OpenVPN log file on the client and server, or run the client with increased verbosity openvpn --config client.ovpn --verb 4. Search for TLS-related errors like “TLS Error” or “certificate verify failed.”
Can clock drift cause TLS handshake failures?
Yes. If client and server clocks are out of sync, certificate validity checks may fail, causing the handshake to fail.
Should I use TLS-auth or TLS-crypt?
Yes. They add an extra layer of authentication for the TLS channel, reducing the chance of certain attacks and helping diagnose issues.
What if certificates are expired?
Renew and replace the expired certificates, ensuring the full trust chain CA -> server -> client is updated on both sides. Tp Link VPN Not Working Here’s How To Fix It: Quick Solutions, Pro Tips, And Real-World Fixes
How do I verify that the CA and certificates match?
Check that the CA certificate used by the server is the same CA that the client uses to verify the server’s cert. The certificate chain should be valid and trusted by the client.
Can a firewall block OpenVPN handshake?
Yes. If the UDP port used by OpenVPN is blocked, the handshake will fail. Ensure the port is open and allowed through the firewall.
What is the difference between UDP and TCP for OpenVPN?
UDP is typically faster and better for real-time data, but TCP can be more reliable across restrictive networks. If you’re having handshake issues, temporarily switching to TCP can help diagnose network problems.
How do I securely rotate certificates without downtime?
Set up new certificates with a new CA or same CA but new certs, distribute the new CA if needed, and gradually switch clients to the new certs while keeping the old ones valid for a short overlap period.
Why do I still see TLS handshake failures after fixes?
Sometimes multiple issues align—certificate chains, TLS versions, and firewall rules. Re-do a clean end-to-end check: verify clocks, reissue certs, confirm configurations on both ends, and test with verbose logging. Proton vpn on linux mint your complete setup guide
If you’re ready to take your VPN setup to the next level, I’ve got a resource that can help you stay secure and fast. Click here to explore one of our trusted recommendations and enhance your VPN experience: NordVPN
Sources:
翻墙 mac:完整指南、工具選擇與實用技巧,讓你快速上手 VPNs
Nordvpn dedicated ip review: Comprehensive guide to dedicated IPs, pricing, setup, and performance for 2025
Best vpns for your vseebox v2 pro unlock global content stream smoother
Windows 11でvpn接続を劇的に速く!デスクトップショートカットと最適化テクニック How to say goodbye to Proton VPN your ultimate guide to cancelling subscriptions deleting accounts and full uninstallation
Vpn稳定的关键因素:在不同场景下实现持续、低延迟的VPN连接指南

Layla Nasser has been writing about consumer technology since 2018, with bylines covering secure messaging, privacy law, and DNS-over-HTTPS. Approaches each review by setting up the product the same way a typical reader would and recording every snag along the way.